Customer Session Popup
Your customers get a clear warning before their session ends, instead of finding a login form in the middle of what they were doing. Active shoppers stay signed in, and anyone who is signed out comes back to the page they were on.
Latest version: 1.0.0 — changelog
Who it's for
- Stores behind the full page cache or Varnish. Pages served from a cache never reach Magento, so they never extend a session. This module keeps the countdown true on those pages.
- Stores with a fixed idle limit. Customers on shared computers are signed out when the limit says so, and the limit holds on the server even with no script running.
- Hyvä stores, including strict Content Security Policy themes. A CSP-safe companion module covers Hyvä 1.3 to 1.5.
- Stores on the free
qoliber/m2-customer-timeout-popup. Saved settings are imported when you upgrade.
Why it matters
- Fewer surprise sign-outs. Customers are told before a session ends, and told when it has.
- Nobody starts over. "Sign in again" returns customers to the page they were on.
- Less interruption for people who are shopping. Scrolling, typing or clicking renews the session in the background, so only customers who are really idle see the warning.
- An idle limit you can rely on. A session past its limit cannot open a page or make a REST or GraphQL call.
- Fewer questions about session length. The admin shows the lifetime your store really runs on, and says when garbage collection cuts it short.
See it in action
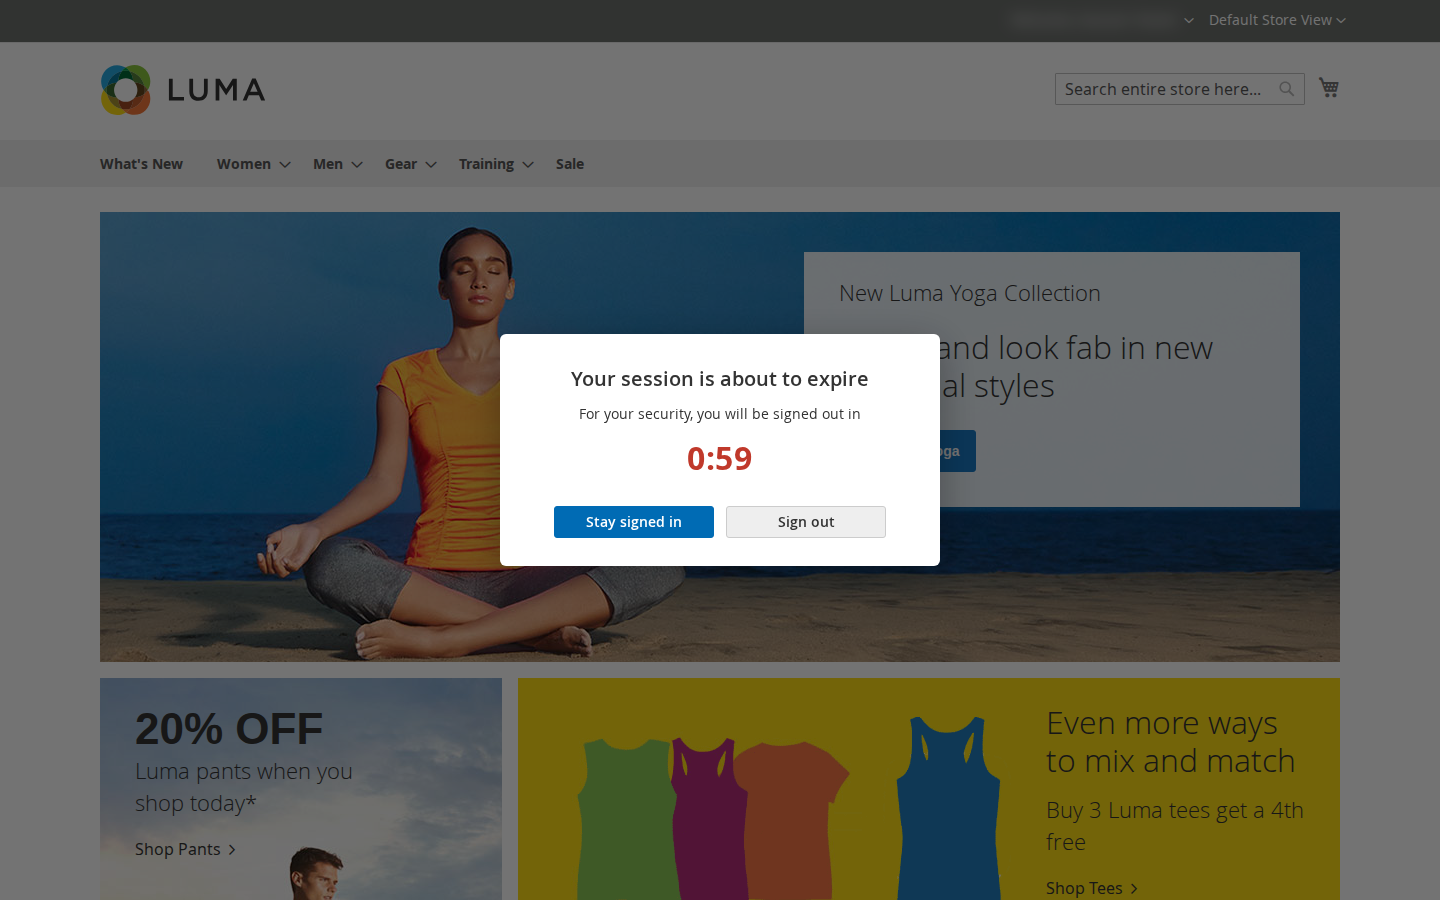
A one-minute warning on a ten-minute session. You set Session Lifetime to 600 and Warn Before Expiry to 60.
Nine idle minutes in, the warning opens at about 0:59, "Stay signed in" has focus, and the browser tab title starts
with the time left.
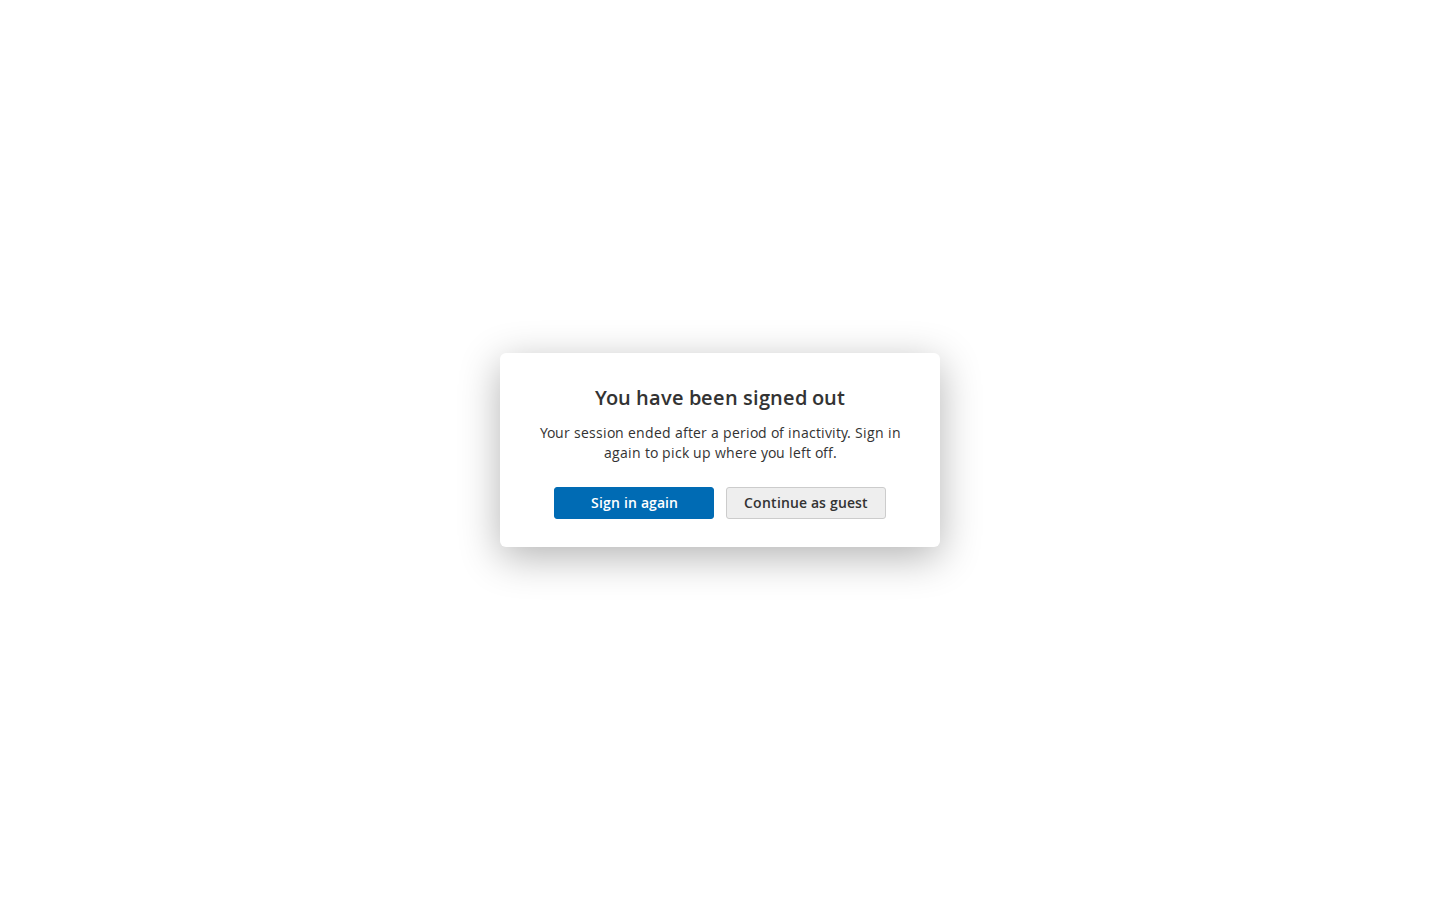
A customer who reaches zero. A customer reading women.html is signed out on the server and told so. "Sign in
again" opens the login form and brings them back to women.html.
Sessions that end sooner than expected. With a cookie lifetime of 3600 and garbage collection at
session.gc_maxlifetime = 1440 on file sessions, the admin reports 1440 seconds and names the 3600 seconds cookie
lifetime beside it. The popup counts down from the shorter value.
Features
| Feature | Benefit |
|---|---|
| The session warning | Customers see the time left and can stay signed in with one click, in every open tab |
| Keeping active customers signed in | People who are using the store are never interrupted by a warning they do not need |
| When a session ends | Customers are told what happened and can return to the page they were on |
| Changing the popup text | Every text can say what you want it to, per store view, with translated defaults when left empty |
| Session lifetime detection | Files, database, Redis and memcache lifetimes are detected and explained in the admin, so you can see why sessions end when they do |
| Server-side idle limit | The limit is enforced before every storefront action and every REST or GraphQL call made with the session |
| Accessible dialog | Focus stays inside the warning, Escape means stay signed in, and screen readers hear the time left at one minute, 30 seconds and 10 seconds |
Competing solutions
The right-hand column describes common practice on the extension market, not any particular vendor.
| Qoliber | Typical marketplace extension | |
|---|---|---|
| GitLab access | Full access to the module's GitLab repository — source, history, issues and merge requests | Varies by vendor |
| Packagist installation | Installed and updated with Composer from our private Packagist (qoliber.repo.packagist.com) as qoliber/customer-session-popup | Varies by vendor |
| Slack access to the development team | A shared Slack channel with the developers who build and maintain the module | Usually ticket-based |
| Unit tests | 65 PHPUnit unit test methods (15 classes) in the repository | Not typically published |
| Integration tests | 65 Magento integration test methods (13 classes), run before every release | Not typically published |
| E2E Playwright tests | 58 Playwright end-to-end test definitions (7 spec files) on Luma and Hyvä, run before every release | Not typically published |
| Documentation | Full docs portal: install, configuration, usage, troubleshooting, developer guide | Varies by vendor |
| Hyvä support | A dedicated Hyvä module for Hyvä 1.3 – 1.5, with Tailwind CSS 3 and 4 builds | Varies by vendor |
| PHP / Magento range | PHP 8.1 – 8.5, Magento Open Source and Mage-OS 2.4.6 or later | Varies by vendor |
What sets it apart
- Hyvä-native. The companion module is a CSP-safe Alpine.js component that shares the base module's session clock.
- No SaaS. Everything runs inside your store. There is no external service and no account to create.
Good to know
- Adobe Commerce, Hyvä Checkout, Mage-OS 3.6 and 4.0, clustered Redis and CDNs in front of the store have not been tested. PWA storefronts are not supported.
- When sessions never time out, the popup stays hidden unless you set a Session Lifetime.
- Keep Session Lifetime longer than your slowest off-site payment. A customer returning past the limit is signed out like anyone else.
Supported versions: PHP 8.1 to 8.5 on Magento Open Source or Mage-OS 2.4.6 and later (magento/framework ^103.0).